You know where the problem is.
Each flaw comes with its address — in code, the file and the line — and the path from outside in to it. Your team opens the report next to the system and checks.
See the report →
SVO audits your company's code and/or servers and delivers, in writing, where each flaw is and how someone reaches it — so your team fixes it first.
Why now
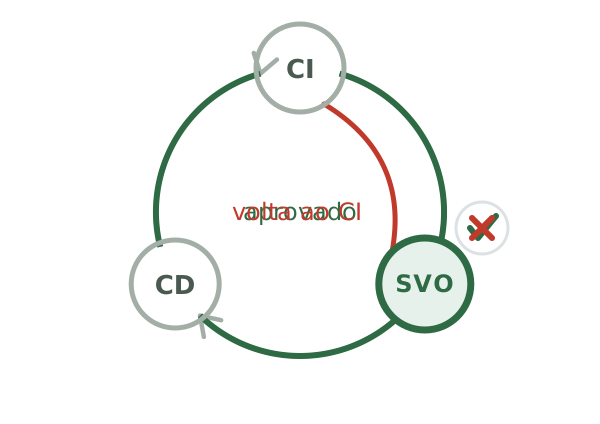
Your development cycle got shorter. So did the cycle of the people looking for flaws. Both ends got faster at the same time, and anyone reviewing their own code at the old pace is racing against a new clock.
Every month a new flaw shows up in software that thousands of companies use — and almost always it was already there, in the code, long before anyone found it.
While it waits, the system works, the tests pass and the dashboard stays green. The cost arrives on the day of the incident: customer data exposed, a system down, a contract at risk — and the conversation with whoever trusted you.
Whoever finds it first decides what happens next.
See what is at stake →What changes with SVO
Each flaw comes with its address — in code, the file and the line — and the path from outside in to it. Your team opens the report next to the system and checks.
See the report →In your environment, with your access — or on our infrastructure: you send the address of the code and the report arrives in your inbox.
See both paths →For code it comes from a free measurement of the project's size; for sites and servers, from the table.
See the table →The proof
The method has already found flaws in public software used by other companies: 9 of them already fixed and published, 4 with CVE, and another 6 on the way. Among those that publish a count alone, they add up to more than 950 thousand installations — systems that may well be running on your server right now, and that today already have a published fix.
Anyone can check it by the number.
The AI is the same for everyone; the method is ours.
When is the right time
From your site seen from the outside to the whole server — you choose how far.
See the products →How it starts
Tell us what you want audited — a site, a system, a server.
Get the price. For code, it comes from a free measurement.
Approve it, and get the report.
What always holds
Any secret found goes into the report masked.
Each customer's report stays with the customer. When the audit runs on our infrastructure, it arrives together with the data destruction certificate — which states, in writing, what was destroyed and what it does not cover.
You get back what the audit covers, where it stops, and the price.